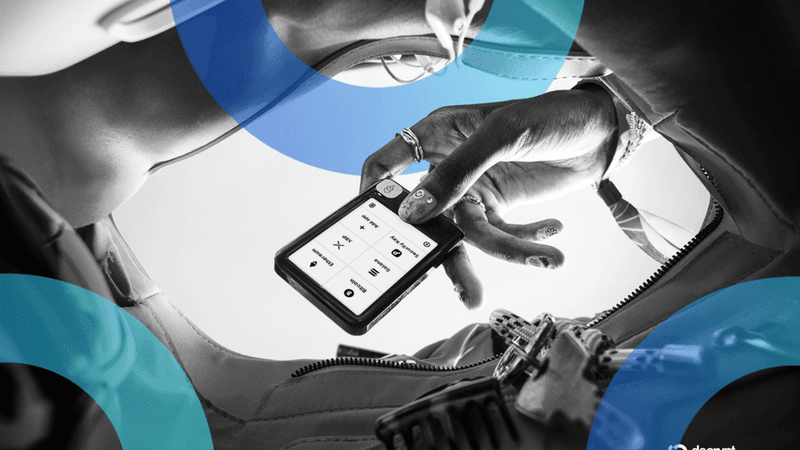
Ledger, the Paris-based hardware-wallet manufacturer, announced that it has instructed the Southeast Asian reseller CryptoBilis to halt all sales and shipments of its devices. The move follows reports that customers who purchased Ledger products through the reseller experienced significant fund losses.
Advisory to affected customers
The company’s support account on X warned anyone who bought a Ledger from CryptoBilis within the past three months to avoid setting up the device. For users who have already initialized their wallets, Ledger recommends transferring assets to a fresh device that uses a new recovery phrase, thereby generating a brand-new set of private keys.
Scope and scale of the alleged theft
Independent blockchain researcher known as Specter traced more than $86 million in suspicious activity across several major networks, including Ethereum, Bitcoin, TRON and the stablecoin USDT. Data from Arkham Intelligence, cited by the analyst, breaks down the estimated loss to roughly $42 million in ETH, $17.6 million in BTC, $16.5 million in USDT and the remainder in other tokens. Ledger has not confirmed the exact figure or the cause of the compromise.
Potential attack vectors
Hardware wallets are designed to keep private keys offline, yet a device compromised before reaching the buyer—such as one pre-loaded with a known recovery phrase—could expose users to immediate drain of funds. No definitive evidence of tampering has been released, and Ledger has not identified how many customers are directly impacted.
Context within the broader security landscape
The incident arrives amid a spate of high-profile crypto breaches. Last month, the exchange Bitget suffered a hack estimated at $387 million, an attack linked to North Korean actors. Similar large-scale exploits have struck platforms on Solana and Blockstream’s Liquid sidechain. Competitor Trezor has also faced recent security setbacks, including data exposure through a shipping partner and an email breach.
Next steps for Ledger and users
Ledger said the pause on CryptoBilis sales will remain in place until the investigation concludes. The firm is working with on-chain analysts to map the flow of the stolen assets and to determine whether the compromised hardware is the root cause. Customers are urged to monitor official Ledger channels for updates and to follow best practices for securing seed phrases.
Why it matters
The episode underscores the persistent vulnerability of supply-chain processes in the crypto-hardware market. Even devices marketed for offline security can become vectors for large-scale theft if compromised before delivery. The incident also highlights the importance of rapid community reporting and forensic blockchain analysis in identifying and containing cross-chain attacks. For the broader ecosystem, the case may prompt manufacturers and resellers to tighten verification protocols, reinforcing trust in hardware-wallet solutions that many investors rely on for safeguarding digital assets.