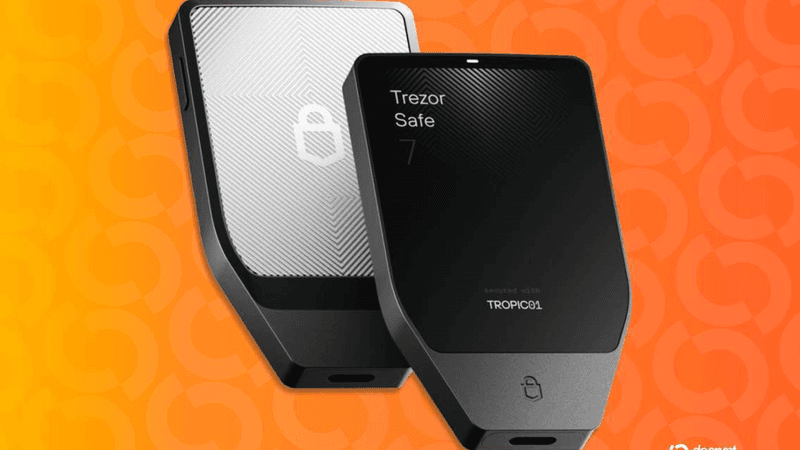
Trezor disclosed that it will cease providing fresh inventory to a selection of its authorized distributors, setting a termination date of 1 January 2027. The move follows Ledger’s recent finding of a covert LTE-based module in hardware wallets sold by a Southeast Asian third-party retailer, prompting heightened scrutiny of the hardware-wallet supply chain.
Trezor reduces its reseller footprint
In a short message posted on X, Trezor explained that the decision is a precautionary step intended to tighten oversight of the devices it ships. The company said there is no evidence that any of its own wallets have been tampered with, but it will now limit the number of partners it can monitor closely. A letter sent to affected distributors states that they will no longer receive new units after the 2027 deadline, though they may continue to sell existing stock through the holiday period. Trezor did not disclose the exact number of resellers impacted, noting that each market was evaluated based on revenue potential and the company’s direct presence.
Ledger uncovers an LTE spy implant
Ledger’s Donjon security team reported that hardware wallets purchased from CryptoBilis, a reseller operating in Southeast Asia, contained an unauthorized component. The module reads the screen when the 24-word recovery phrase is displayed, decodes the phrase, and then transmits the data over an LTE connection using an embedded eSIM. The implant does not alter the secure element that stores private keys nor the device’s firmware, meaning the compromised units appear and function normally. Ledger warned anyone who bought a wallet from CryptoBilis within the previous 90 days not to initialize the device, and advised users who had already done so to move funds to a fresh seed phrase generated on a verified Ledger device.
Broader implications for hardware-wallet security
Both firms have reiterated the importance of acquiring wallets only from official outlets or vetted resellers. Trezor’s earlier warnings about counterfeit models on a Russian marketplace and a data breach involving its shipping partner underscore the ongoing challenges of protecting the hardware-wallet ecosystem from supply-chain attacks. The combined actions of Trezor and Ledger signal a shift toward stricter distribution controls, aiming to reduce the attack surface for malicious actors seeking to embed hardware backdoors.
Why it matters
The hardware-wallet market underpins the security of billions of dollars in crypto assets. A single compromised device can expose a user’s master seed, granting an attacker unrestricted access to all holdings. By tightening reseller relationships, Trezor hopes to better audit the provenance of each unit, while Ledger’s public disclosure of the LTE implant raises awareness of novel exfiltration techniques. Together, these developments may push the industry toward more transparent supply chains and stricter verification standards, protecting end-users from increasingly sophisticated hardware threats.